Integration documentation that stays current
TrueStateRegistry discovers the integrations in your configured Azure and Azure DevOps scope and regenerates the catalog, diagrams and change history on every deploy. Developers complete one small, policy-validated manifest.
About 5 minutes per integration, once · Updated on every deploy
Docs go stale because developers hate maintaining them
Your integration docs were accurate once the day someone wrote them. Now it’s 2 a.m., something’s broken, and nobody can see what talks to what, who owns it, or what changed. The new engineer spends months rebuilding the picture the last one took with them.
Developers touch one small file. The pipeline does the rest.
Each integration is one small YAML file with eight mandatory fields: id, name, criticality, data classification, support contact, source, target, and a one-line description. Everything else is optional. Validation names the missing field in plain language, never a stack trace.
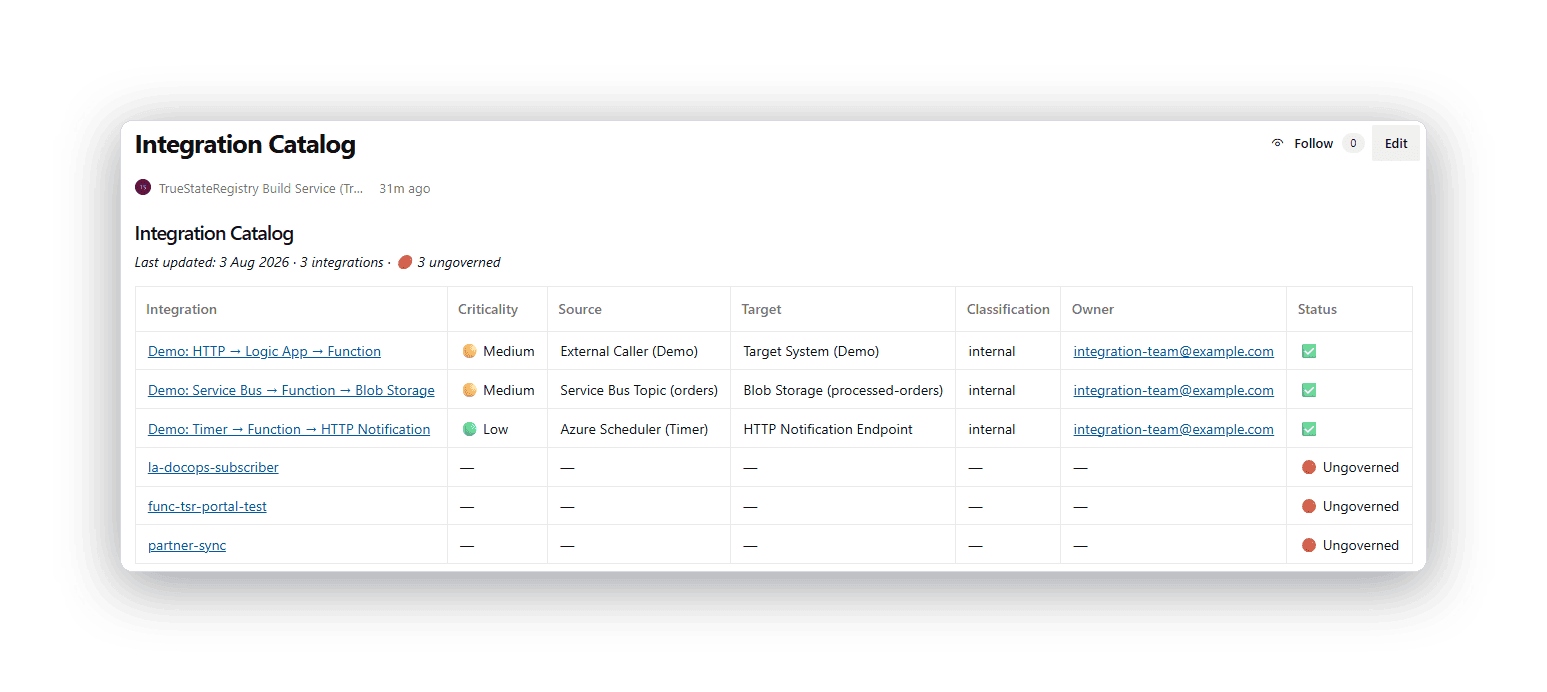
One table with the integrations in your scope
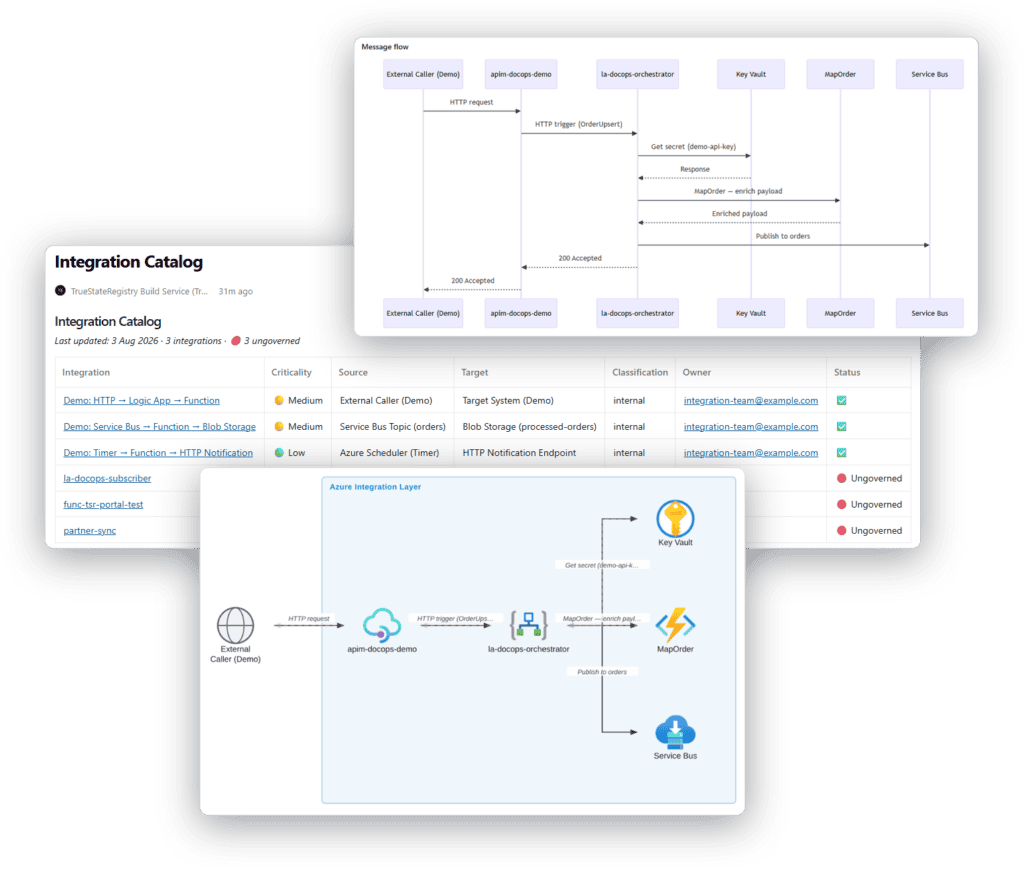
The catalog lists every integration with its flow, owner, criticality, data classification and governance status. Sortable, current as of your last deploy. It’s the answer to “what do we actually run?” a question most teams can’t answer without a week of digging.
The one screen a CISO or auditor reads first
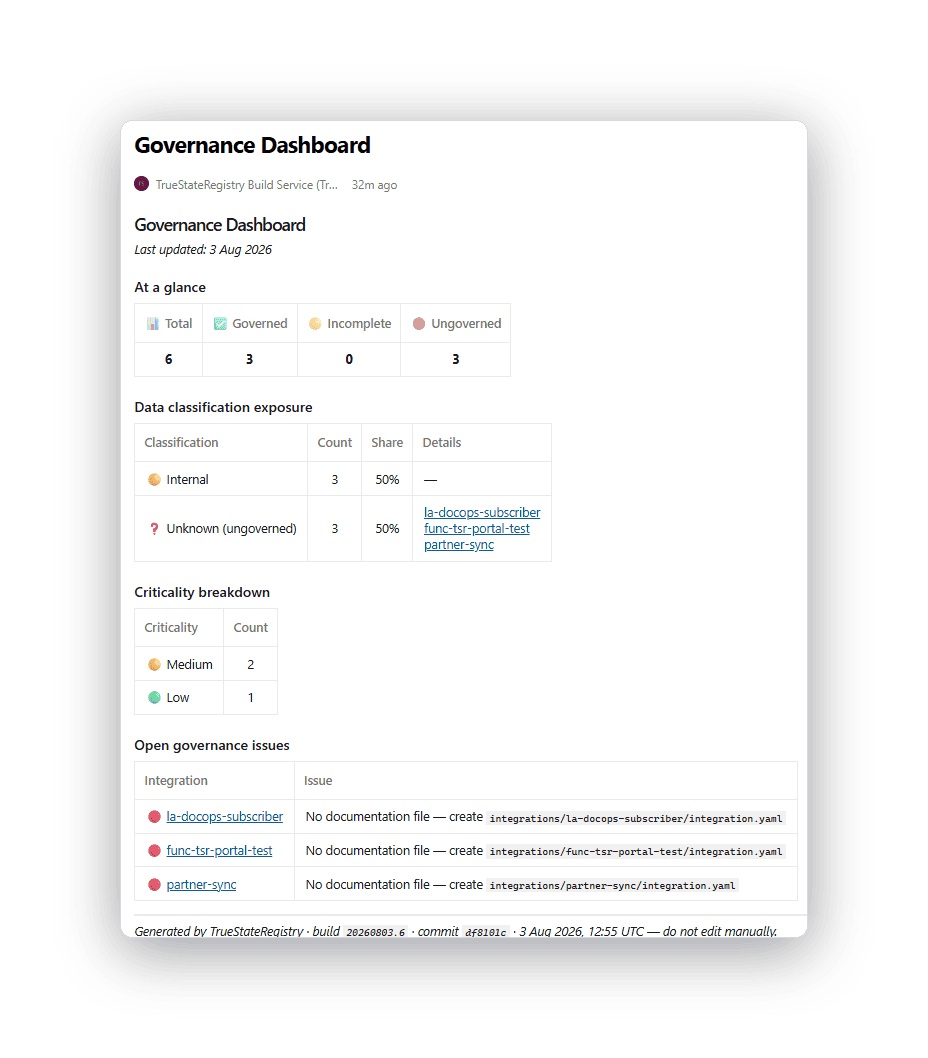
Posture at a glance: how many integrations are governed, which touch Restricted or Confidential data, what’s critical, and every open gap with the exact missing field. Green is comfort. Red is the work you didn’t know you had.
Every integration gets its own page with real diagrams
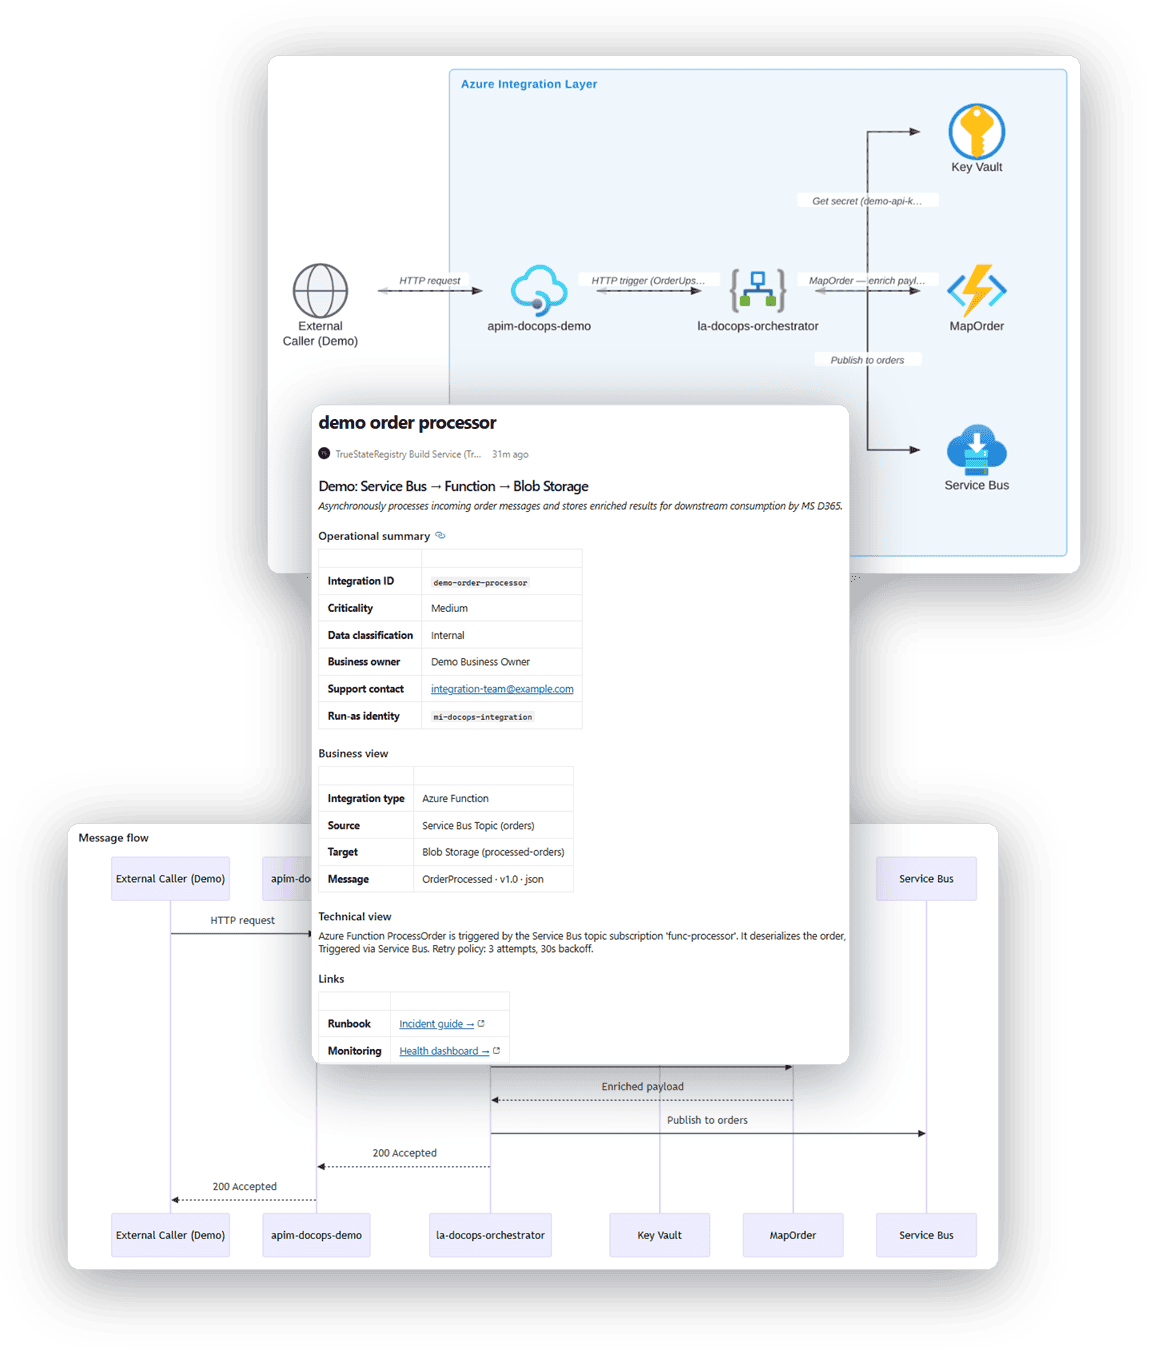
An architecture diagram drawn with actual Azure service icons, and a message-flow sequence discovered from the Logic App workflow itself. Plus the business purpose, technical notes, sample payloads, and links to the runbook. Generated, not drawn by hand.
Who changed it, when, and who approved it
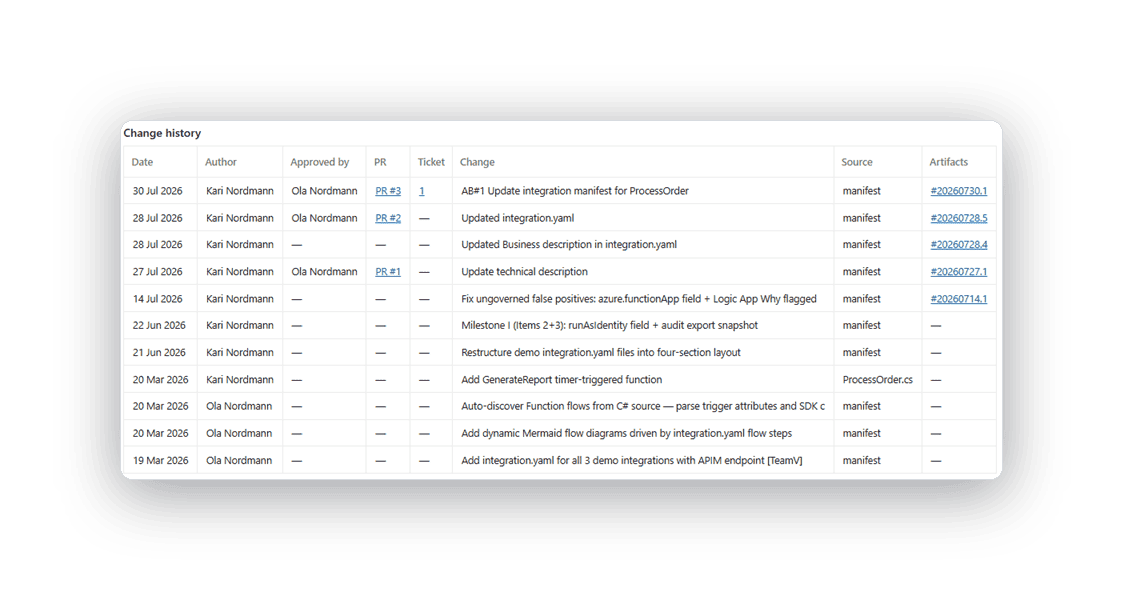
Every change to an integration, pulled from git and its pull request: the date, the author, the approver’s name, and the PR number on the integration’s own page. The evidence exists because of how your team already works.
How it works
Live in three steps, then automatic
Step 1
Add one pipeline to your Azure DevOps project and point it at your resource groups and repos. No platform to host, no agents.
Step 2
It discovers your Logic Apps, Functions and repos, and opens a pull request with draft manifests. About five minutes each to complete.
Step 3
It runs on every deploy, regenerates the catalog, dashboard, diagrams and pages, and flags anything ungoverned.
Runs where your data already lives
In your tenant
Everything runs in your Azure environment. Customer data sent to TrueStateRegistry-hosted services is zero. No telemetry, no licence-server calls.
Keeps secrets out of its output
It does not read Key Vault, app settings or access keys. Every published page, diagram and CSV passes through redaction: known secret patterns and internal hostnames are replaced. You can also set the build to fail when one is detected.
Least privilege
Read-only on Azure: Reader on the resource groups in scope, and read access to the repos. By default it writes only your wiki pages and pull requests for new manifests.
Verifiable
Every page carries the build ID, commit SHA and timestamp that produced it.
A snapshot is out of date by the next deploy
Evidence assembled by hand goes stale with the next release. TrueStateRegistry regenerates it on every deploy, so the answer is current as of your last deploy and the same every time you ask.
FAQs
What setup looks like
Requirements
- An Azure DevOps project with Wiki enabled, and someone with Project Administrator rights for the setup
- A YAML pipeline for TrueStateRegistry
- Reader on the resource groups in scope and read access to the repos, through the pipeline’s service connection
Example manifest
The eight mandatory fields, plus the business owner the default governance policy asks for.
integrationId: contoso-orders-to-crm
name: Contoso Orders to CRM
criticality: medium
dataClassification: internal
owners:
  supportContact: integrations@contoso.example
  businessOwner: Head of Sales
systems:
  source: Contoso Orders
  target: Contoso CRM
description:
  business: Sends confirmed orders to the CRM.
What gets written
- Wiki pages: the catalog, the governance dashboard and one page per integration with its change history
- A dated ZIP and CSV as a pipeline artifact
Further reading
Segregation of Duties in Azure DevOps: Proving Who Approved What
Founding pilot
Try it on your own estate. Free for 30 days.
Add one pipeline. TrueStateRegistry discovers your Logic Apps and Functions, compares what it finds with your current integration list, and you get a dated audit pack.
Free. No contract. You keep what it finds.
Your effort: one pipeline and two short check-ins.
Hands-on setup with the engineer who built it, and a direct say in the roadmap.
Prefer to see it first? Book a 30-min walkthrough